
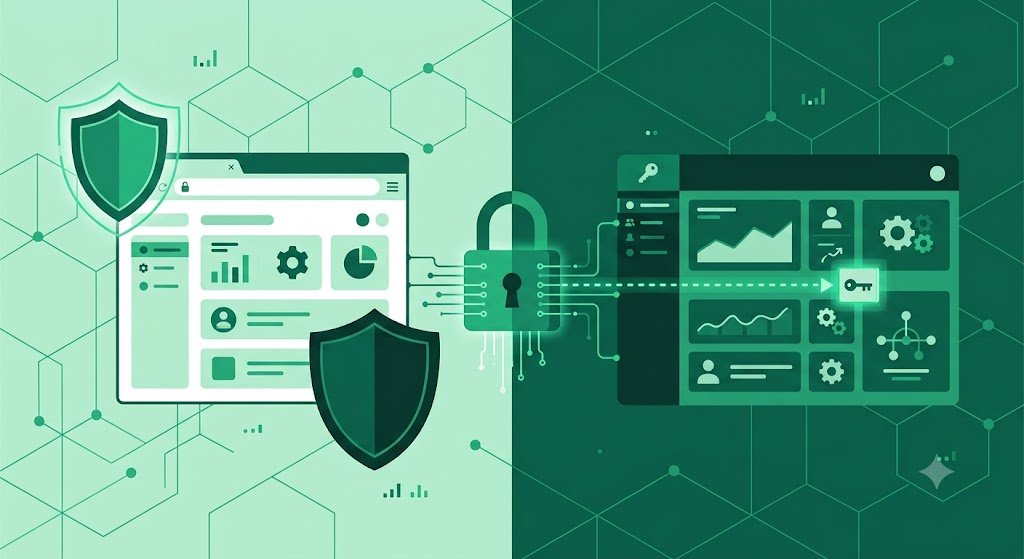
Core provides dynamic access control, CSRF, session fingerprinting, path guard, brute-force tracking, private storage, and packet validation. This feature is a layer, not a guarantee of deployment security.
Authentication and dashboard
The PHP dashboard is outside the web root and can only be reached via the router admin_path. The wrong path is masked as a frontend 404. Login uses CSRF, PHP password hash, and configurable test protection. Hidden paths reduce scanning noise, but do not replace unique passwords, rate limiting proxies, or MFA from additional integrations.

Sessions and HTTPS
Cookies can use HttpOnly, SameSite, domain/path, and Secure according to configuration. Set FORCE_HTTPS=1 only after the proxy/web server forwards the HTTPS status correctly. Protect cfg/.env, session secret, secret token file, and database credentials.
Authorization
Use least privilege. Site Owner is an additional boundary for critical operations; Ordinary admins are not identical to owners. Permissions, scope, ownership, account status, and guard routes are checked server-side. ACL plugins add conditions, not bypass Core guards.
Assets and operations
Private assets must be on a private disk with the right scope. PDF viewer tokens are temporary and not public links. Update only from trusted endpoints/packages, check checksums/manifests, and create tested backups. Patch PHP, database, web server, themes and plugins regularly. Monitor error logs and audit authorization without saving secrets to the log.