
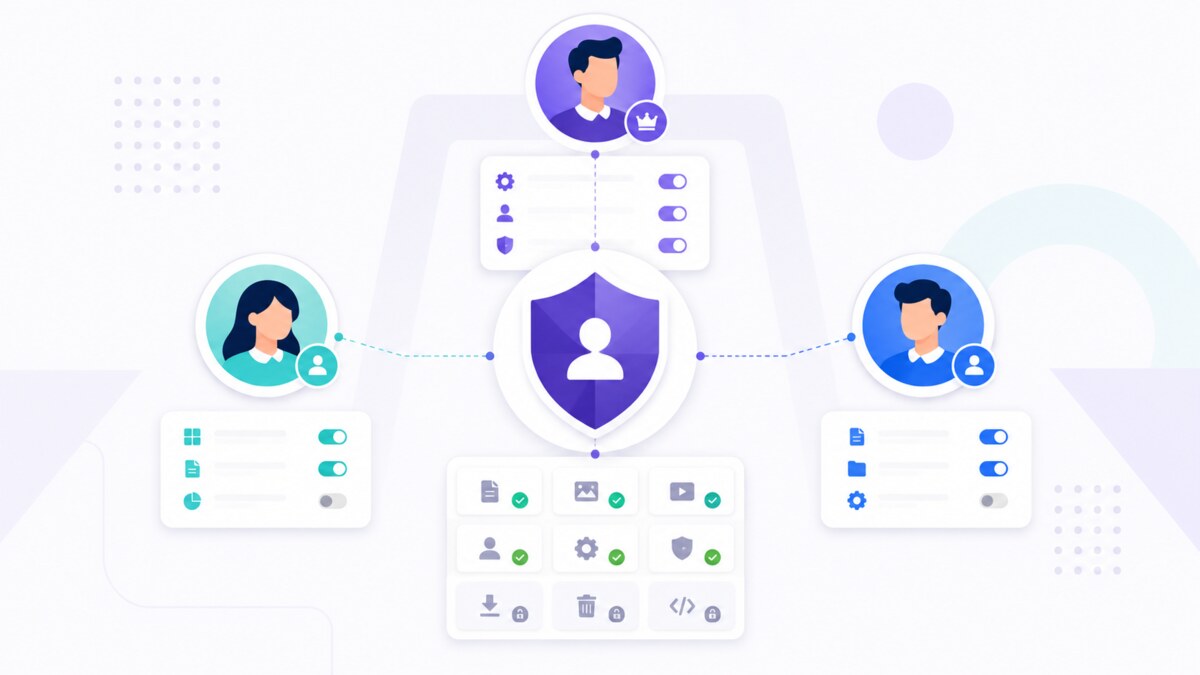
Roles & Permissions combines grants from all active user roles. This menu is restricted to Site Owners; Route permissions are still checked server-side.

System roles
Author, Editor, and Administrator are provided Core. Slug, base rank, and grant Core system roles are schema/migrated reconciled so that basic policies remain consistent. Use custom roles for a variety of tasks, rather than relying on re-alignable role system grant modifications.
Permissions and scope
The permission key states the action. supports_scope states whether the action requires an owner context. Scope Own limiting own resources; Same or Lower compare authority rank owners; Any includes all resources; Global for actions without an owner. Rank does not provide access without permission.
Custom roles
- Create a stable slug and minimum rank.
- Enable only the permissions needed.
- Select the smallest scope for scoped permissions.
- Assign the role to the user, then test with that account.
Permissions that have not been fully migrated may appear as unavailable for custom roles. Inactive grants are maintained so they don't disappear quietly. Plugin permissions can also be nondelegable so that only the default system role can receive them.
Changes in roles and permissions trigger audits/hooks after transactions. The core rechecks sensitive mutations to reduce races when access changes occur simultaneously.