
Jyavani Core 2.3.74 uses dynamic roles and permissions. The old role fields remain synchronized for compatibility, but new access decisions must use effective permissions and scope.
SiteOwner
Site Owner is a special account attribute, not a role. Foundation marks the initial account as Site Owner, gives the legacy admin role, and installs the system Administrator role. The most sensitive operations such as Roles & Permissions and Core updates require Site Owner in addition to related permissions.

System roles and custom roles
- Author: grant Core mainly for its own content.
- Editor: inherit the Author's foundation and receive additional editorial grants.
- Administrator: grant active Core broadly, but not automatically Site Owner.
Custom roles start without a grant. Permission scopes can use Own, Same or Lower, or Any; Non-resource actions use Global. Authority rank only affects Same or Lower and does not provide permission by itself.
Account cycle
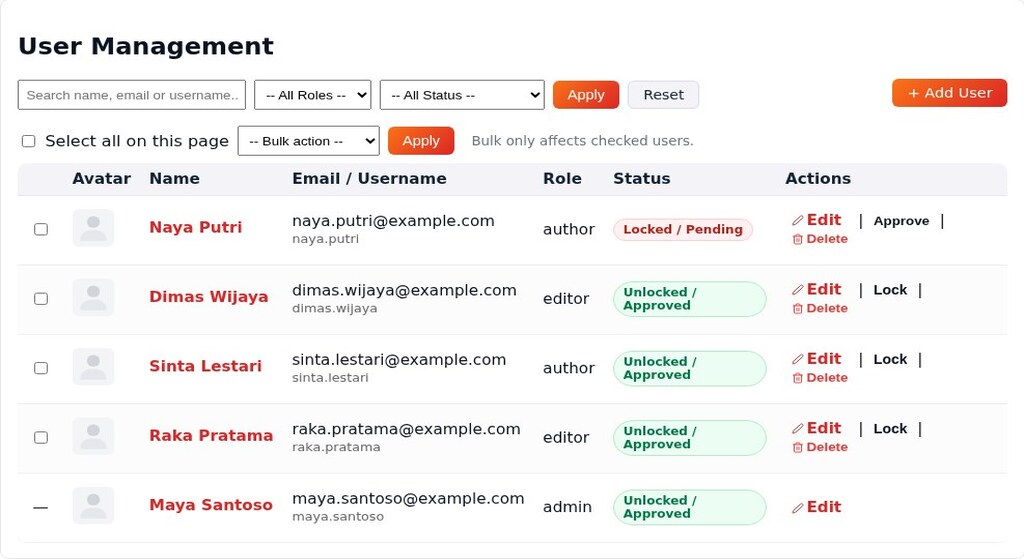
Users can have several active roles. Lock prevents logging in without deleting the account. Delete user using Trash, with separate restore/purge; consider content ownership before purge. Important role changes and authorization operations are recorded in the audit log.
Public registration, when enabled, always installs an Author and can create a locked account when approval is required. Review access with non-owner accounts, not just from the Site Owner view.